“Give me the passwords and clean out your desk.” The Slack message arrived at 8:17 Tuesday morning from Chad Langston, our new vice president of operations. He had copied Human Resources. I read it twice, then looked through the glass wall of his office. Chad had been with Meridian Distribution for eleven days. I had been keeping its technology infrastructure alive for eleven years.
There was only one problem with his order. I was not a Meridian employee. My name is Lauren Mitchell, and I owned Mitchell Systems Group, the outside technology firm responsible for Meridian’s warehouse automation, encrypted archives, logistics databases, disaster recovery network, and several proprietary applications my company had built from scratch.
My desk inside headquarters was part of the service agreement. So was my badge. So was twenty-four-hour emergency access. Employees often forgot the distinction because I attended meetings, drank the same terrible coffee, and knew every department head by name. Chad apparently had never bothered to read the contract before deciding I worked for him.
I typed one sentence back. “Please confirm you are directing Mitchell Systems Group to surrender administrative credentials and immediately cease services.” Thirty seconds later, Chad replied, “Correct. Effective immediately. HR is aware.” Then he added, “Do not make this difficult.”
I forwarded the entire exchange to my attorney, Daniel Ross, along with one line: “I think he just triggered Section 14.” Daniel called less than two minutes later. “Do not give him a single credential,” he said. “And do not leave the building until I call you back.”
Section 14 was Meridian’s protected termination clause. Because our systems controlled regulated customer data and active warehouse machinery, Meridian could terminate our agreement only with ninety days’ written notice, a documented transition plan, and payment of the remaining annual contract minimum. Immediate termination was permitted only after proven fraud, security misconduct, or material breach.
Chad had none of those. Worse, the contract specifically prohibited Meridian employees from demanding master passwords directly. Credentials could only be transferred through a formal security handoff involving my firm, Meridian’s legal counsel, and an independent cybersecurity officer. Chad’s Slack message violated that provision in writing.
At 8:42, HR director Melissa Crane appeared beside my desk looking uncomfortable. “Lauren, Chad says you’re refusing to cooperate.” I turned my monitor toward her and opened the agreement. Melissa read the highlighted paragraph, then slowly stopped talking.
At that exact moment, the warehouse monitoring dashboard began flashing red. Chad had instructed an internal analyst to disable my company’s administrator account. The attempt automatically triggered a security lock on two distribution centers, freezing software access to automated loading schedules.
Melissa stared at the screen. I stared at Chad’s office. Then Daniel called back and said, “Meridian’s general counsel has the message. Don’t touch anything until they arrive. Your new VP may have just turned an improper firing into a multimillion-dollar contract dispute.”
Within fifteen minutes, the atmosphere on the operations floor changed completely. Chad came storming toward my desk with Melissa behind him. “Why are the warehouses locked?” he demanded. I kept my hands away from the keyboard. “Because someone attempted to revoke a protected administrator account without following the transition protocol.”
“I told Jason to remove you,” Chad snapped. “You’re finished here.” Melissa quietly interrupted him. “Chad, Lauren is a vendor.” He looked at her like she had suddenly switched languages. “She has a desk here.” “That does not make her an employee,” Melissa answered.
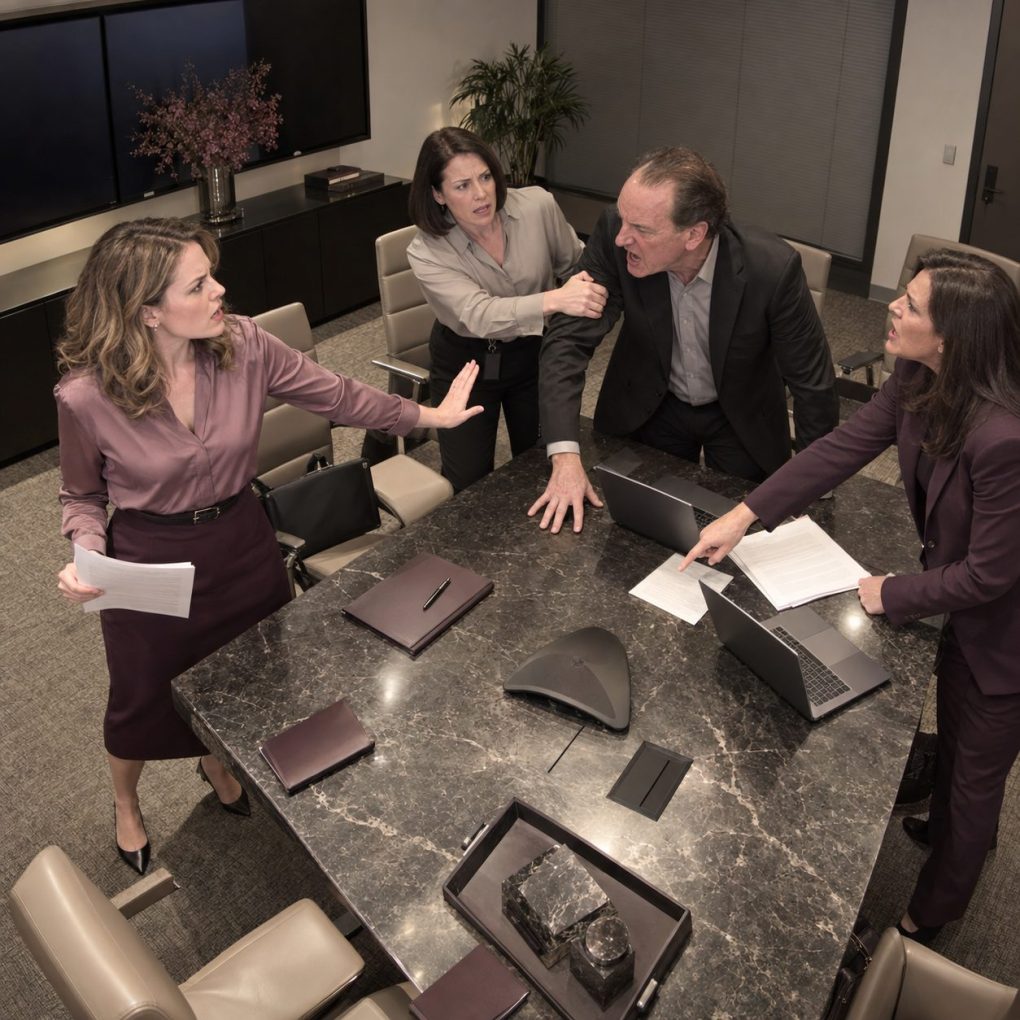
Before Chad could respond, Meridian’s general counsel, Rebecca Sloan, arrived with the chief financial officer. Rebecca asked everyone to move into the conference room. Chad immediately started explaining that he was restructuring operations and eliminating “unnecessary contractors.”
Rebecca placed my contract on the table. “Did you review this before sending your message?” Chad hesitated. “I reviewed the budget.” “That wasn’t my question.” His face tightened. He admitted he had never read the full agreement because he assumed procurement had standard termination language.
The CFO asked what restoring normal warehouse access would require. I explained that my company could restore the suspended accounts immediately, but I needed written confirmation that Meridian was rescinding Chad’s unauthorized termination instruction and that no employee would attempt another credential change outside the contract.
Chad laughed. “This is ridiculous. We own the systems.” I opened the intellectual-property schedule attached to the agreement. Meridian owned its business data. Mitchell Systems Group owned the custom integration software, encryption framework, monitoring tools, and deployment architecture. Meridian had a renewable license to use them while the contract remained active.
That was the part Chad had completely missed. He had assumed firing me meant keeping everything my company had built. Under the agreement, Meridian could transition to another vendor, but it required months of documentation, licensing negotiations, security audits, and technical migration.
Rebecca asked me to step outside while Meridian’s executives discussed the situation. Twenty minutes later, she invited Daniel into the meeting by video call. Chad was no longer sitting at the head of the table.
Meridian rescinded his directive in writing. I restored warehouse access at 10:06. No shipments were lost, but several loading schedules had been delayed. More importantly, the automated security log showed exactly who had attempted to disable my account and exactly when Chad had authorized it.
Daniel then raised another issue. Chad’s demand for master passwords potentially violated Meridian’s own cybersecurity policy, because those credentials provided access to customer financial records and encrypted commercial files. Rebecca’s expression changed immediately.
By lunchtime, what Chad had intended as a quick removal had become a formal internal investigation involving legal, compliance, procurement, cybersecurity, and the executive team. I returned to my desk, opened my laptop, and continued working under the same contract he had tried to terminate two hours earlier.
The investigation lasted twelve days. During that time, Chad was prohibited from issuing instructions to outside technology vendors without legal approval. He stopped walking past my desk entirely. The confidence he had displayed during his first week disappeared whenever Rebecca entered a meeting.
The deeper review uncovered why he had wanted me gone so quickly. Chad had already promised Meridian’s CEO that he could cut technology costs by nearly forty percent within his first quarter. His plan depended on replacing several specialist vendors with cheaper contractors recommended by a former colleague.
My company was the largest contract on his spreadsheet. Chad believed he could cancel it immediately, transfer our passwords to his replacement vendor, and claim the savings before anyone questioned the technical consequences.
There was no secret conspiracy and no dramatic criminal scheme. It was simpler than that. Chad had made an expensive executive decision based on assumptions, then tried to force reality to match his spreadsheet.
Meridian’s board reviewed the situation because our agreement represented essential operational infrastructure. Daniel negotiated directly with Rebecca. We did not demand revenge. We demanded clear procedures. Meridian agreed that all future vendor terminations involving critical systems would require legal and cybersecurity review before operational action.
They also amended our contract. The remaining term was extended for eighteen months, our transition protections were strengthened, and Meridian paid the emergency-response charges caused by the unauthorized account shutdown. They also covered my legal expenses under the indemnification clause Chad had accidentally activated.
Chad remained with the company, but he lost direct authority over cybersecurity vendors and technology procurement. The CEO reportedly gave him a simple instruction: understand a contract before attempting to terminate it. I never asked for more details because they were not necessary.
Three weeks later, Chad finally approached my desk. His voice was much quieter than it had been that Tuesday morning. “I owe you an apology,” he said. “I thought you were refusing an executive directive.” I answered, “I was refusing an unauthorized request for protected credentials.”
He nodded. “I understand that now.” Then he asked whether I would meet with him and explain how our systems actually worked. I agreed, but I brought our technical director and documented the meeting like every other vendor session.
The strange part was that I never enjoyed watching Chad get embarrassed. His mistake could have disrupted hundreds of warehouse employees who had nothing to do with our disagreement. That was why the contract had those safeguards in the first place.
Six months later, Meridian renewed our agreement again. The original Slack message still exists in my legal archive. Whenever a new executive asks why our termination procedure is so detailed, I do not tell them the whole story. I simply say, “Because passwords are not employment property, vendors are not employees, and expensive systems should never depend on someone reading only the first page of a contract.”