“They thought cheating an expert out of their earned fee was a smart business move. They didn’t realize the kill switch was already activated.”
“Here’s your payment.”
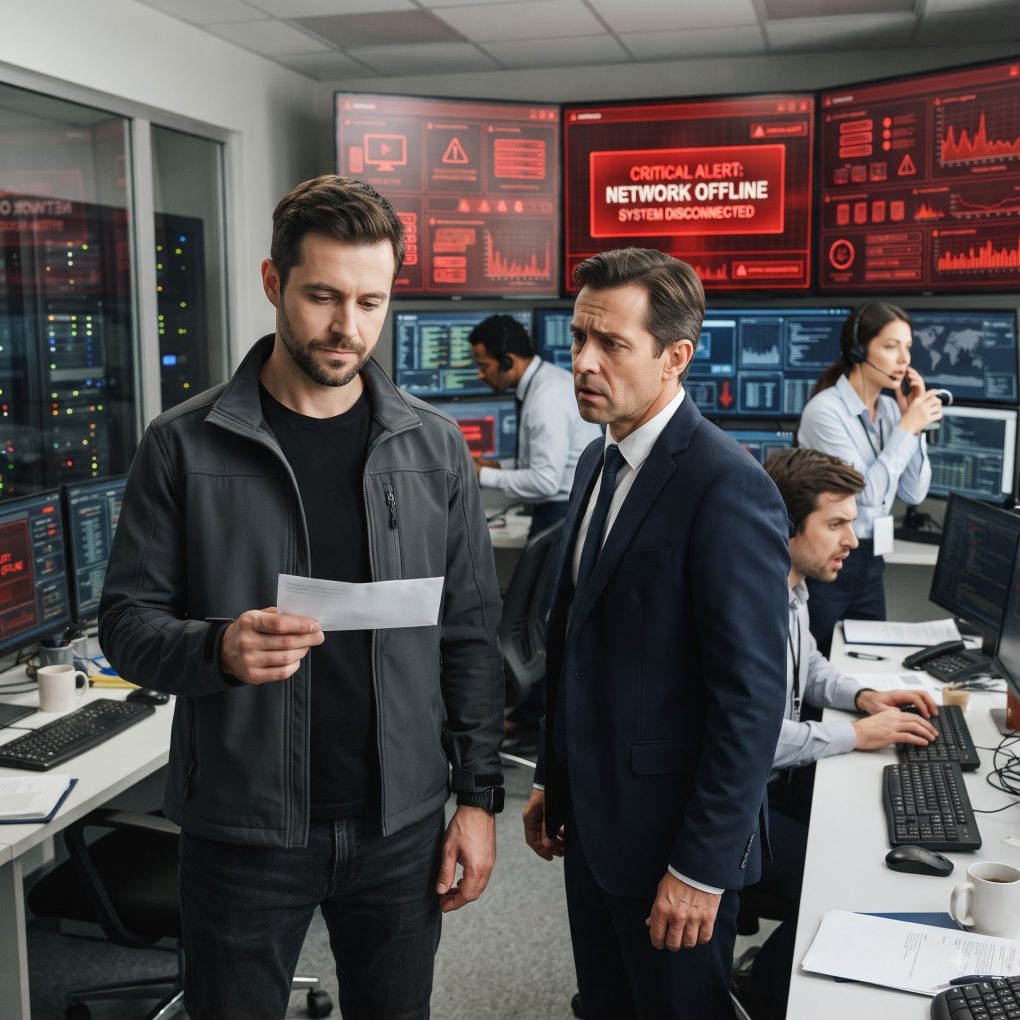
The CFO dropped a tiny envelope onto the conference table.
I opened it.
Inside was an $800 cashier’s check.
I stared at him.
“You agreed to pay me $800,000.”
He shrugged.
“That was before we realized how desperate you were.”
Across the room, three executives avoided my eyes.
Desperate?
Their $300 million enterprise system had been completely locked down after a catastrophic migration failure.
For nine days, their engineers had tried to recover it.
Nothing worked.
Then they called me.
I had designed the original recovery architecture years earlier, before they replaced me with a cheaper contractor.
Their attorney had negotiated an $800,000 emergency recovery fee.
I accepted because the system supported hospitals, warehouses, payroll processors, and thousands of employees.
People were waiting.
I worked for thirty-six straight hours.
I found the corrupted index, rebuilt the recovery path, and restored the critical servers.
By midnight, their executives were celebrating.
By morning, they were renegotiating my invoice.
Now I was standing there holding $800.
“I’m not cashing this.”
The CFO smiled.
“Take it or leave it.”
I placed the check back on the table.
“You’ll regret that.”
He laughed.
“Your work is finished.”
I stood.
“Actually, it isn’t.”
His smile disappeared.
I picked up my laptop bag.
“I haven’t activated the final recovery sequence.”
Everyone froze.
The CEO stepped forward.
“What does that mean?”
“It means you have the system running.”
I pointed toward the server dashboard.
“But you don’t have the complete recovery configuration.”
The CFO’s face hardened.
“You’re threatening us?”
“No.”
I looked at the clock.
“I’m warning you.”
Exactly two minutes later, every monitor in the conference room went black.
Phones started ringing.
Then the emergency alarms began.
Someone shouted from the hallway.
“WE LOST EVERYTHING AGAIN!”
The CEO turned toward me.
“What did you do?”
I calmly picked up my coat.
“Nothing.”
Then I looked at the $800 check still sitting on the table.
“You got exactly what you paid for.”
Teaser
They thought humiliating me would save them $799,200. Instead, their entire recovery operation collapsed at the worst possible moment. But the outage wasn’t the real surprise. Before I left that building, I discovered why they had deliberately tried to underpay me—and who had been waiting for the system to fail a second time.
The alarms continued screaming.
Executives rushed into the hallway.
Engineers shouted over one another.
“What happened?”
“Database nodes are offline!”
“The backup cluster isn’t responding!”
“Who changed the recovery configuration?”
I stood beside the conference table.
“I didn’t.”
The CEO, Martin Hale, stared at me.
“You said you didn’t activate the final recovery sequence.”
“I didn’t.”
“Then why did everything shut down?”
I looked at the dashboard.
“Because someone activated the old failover process.”
The room went silent.
The old process had been retired years earlier.
Martin looked at his CTO.
“Who has access?”
The CTO opened his mouth.
Then stopped.
“Six people.”
“Names.”
He listed them.
The CFO.
The CTO.
Two senior engineers.
A contractor.
And me.
Martin looked at me.
“You still have access?”
“Technically.”
“Did you use it?”
“No.”
Then the CTO’s phone buzzed.
He looked at the screen.
His face went pale.
“We’re getting unauthorized login alerts.”
“From where?”
“Inside the network.”
That made no sense.
The primary network was down.
Yet someone was attempting to access the backup environment.
I immediately understood.
“The recovery environment wasn’t compromised,” I said.
Martin turned toward me.
“What?”
“The backup is being attacked right now.”
The CTO stared at me.
“By whom?”
I pointed toward the access logs.
“Someone who knew exactly where the old recovery credentials were stored.”
Then I noticed something else.
The credentials had been accessed before I ever arrived.
That meant the failure had started long before the emergency call.
I opened another log.
There it was.
A scheduled task had been created six days earlier.
It was designed to corrupt the recovery index if the primary system failed.
Martin whispered, “Who created it?”
The CTO checked.
Then looked at the CFO.
The CFO immediately said, “Don’t look at me.”
But nobody moved.
I zoomed in.
The task had been created using a contractor account.
A contractor who had been hired by the CFO three months earlier.
Then the CFO’s attorney suddenly stepped forward.
“You should stop accessing company systems.”
I looked at him.
“I’m trying to keep your company alive.”
He lowered his voice.
“You have no authorization.”
I smiled.
“Then you should probably call the person who authorized me.”
Martin frowned.
“Who?”
I pulled out my phone.
“I’ll show you.”
I opened the original emergency agreement.
There was a clause everyone had overlooked.
My recovery access remained active until the system had passed a final independent stability test.
That test had never happened.
The CFO had tried to pay me $800 and force me out before I could complete it.
And now I knew why.
They weren’t merely trying to save money.
They were trying to make sure I couldn’t discover what had happened inside the system.
Then my phone received a message.
Unknown number.
Stop looking at the recovery logs.
A second message arrived.
You don’t know who you’re protecting.
I looked at Martin.
“We have a much bigger problem.”
Because the person attacking the backup wasn’t trying to destroy the system.
They were trying to erase evidence.
The second message stayed on my screen.
You don’t know who you’re protecting.
I looked at it for several seconds.
Then I turned the phone toward Martin.
He read it.
His expression changed.
“Who sent that?”
“I don’t know.”
The CTO stepped closer.
“Don’t respond.”
“I wasn’t planning to.”
Instead, I took screenshots and forwarded them to my attorney.
Then I turned back to the recovery console.
The network was still unstable.
But the pattern was becoming clear.
Someone had intentionally created a failure inside the recovery environment.
The original outage had been blamed on a migration error.
That was only partly true.
The migration had failed.
But somebody had made the recovery process fail too.
That was the difference between an expensive accident and deliberate sabotage.
Martin finally understood.
“You think someone caused this?”
“I think someone made sure you couldn’t recover from it.”
“Why?”
“That is what we need to find out.”
The CTO pulled up the contractor records.
The suspicious account belonged to a company called Northbridge Systems.
Their lead engineer was a man named Evan Price.
He had worked directly under the CFO for six months.
Martin looked at the CFO.
“Why didn’t I know Northbridge had administrative access?”
The CFO immediately became defensive.
“They were brought in to accelerate the migration.”
“Who approved them?”
“You did.”
Martin shook his head.
“I approved a limited consulting contract.”
He pointed at the access report.
“Not administrator credentials.”
The CTO checked the authorization records.
Then he stopped.
“The credentials were expanded three months ago.”
“Who approved that?”
He looked at the screen.
“The CFO.”
The room went silent.
The CFO’s face hardened.
“This is absurd.”
I said nothing.
I simply opened the access history.
There were hundreds of unusual actions.
Some looked harmless.
Others didn’t.
A backup database had been copied.
A recovery key had been exported.
Several internal credentials had been moved into an encrypted storage location.
And six days before the main outage, someone had created the malicious recovery task.
Martin looked sick.
“Why would anyone do this?”
I answered carefully.
“Money.”
He looked at me.
“Explain.”
I pointed toward the contract database.
“Your emergency recovery agreement with me was worth $800,000.”
“Yes.”
“But your company has cyber-insurance.”
Martin nodded.
“And business interruption coverage.”
“Yes.”
“Someone could make money if the outage became serious enough.”
The CFO immediately shouted, “That’s an accusation!”
I shook my head.
“It’s a possibility.”
But there was another piece.
I opened the procurement records.
Northbridge Systems had received a large performance bonus if the migration was declared a complete success.
If the migration failed, they could lose the contract.
If the recovery failed afterward, they could blame the original system.
And if the company became desperate enough, they could propose an expensive emergency replacement.
Martin stared at the documents.
“So someone created the problem and positioned themselves to sell the solution.”
“That’s what the records suggest.”
Then we found something even worse.
Northbridge wasn’t simply a contractor.
The CFO’s brother owned a minority interest in it.
Martin slowly turned toward the CFO.
“Is that true?”
The CFO didn’t answer.
His attorney stepped forward.
“My client will not answer further questions without counsel.”
Martin nodded.
“Fine.”
He looked at security.
“Escort him from the building.”
The CFO exploded.
“You can’t do this!”
Martin didn’t move.
“You’ve been lying to the board, hiding a conflict of interest, and authorizing access beyond the contract.”
Security escorted him out.
But the network was still down.
The crisis wasn’t finished.
The CTO looked at me.
“Can you restore it?”
“Yes.”
Martin asked, “How long?”
“If nobody interferes, several hours.”
“Do it.”
I hesitated.
“I’ll need written authorization.”
Martin immediately signed it.
“Whatever you need.”
This time, I had full authority.
I isolated the compromised recovery environment.
Then I rebuilt the recovery index from clean snapshots.
I removed the unauthorized credentials.
I created new encryption keys.
I verified the backup chain manually.
The process took hours.
Nobody celebrated.
Nobody left.
For the first time, the executives understood that recovering a system wasn’t about clicking a button.
It was about knowing which pieces could still be trusted.
At 3:17 a.m., the first critical server came online.
Then the second.
Then the third.
The payroll systems came back.
The warehouse systems followed.
By sunrise, most operations had been restored.
The company wasn’t fully operational yet, but the immediate crisis was over.
Martin walked into the server room.
“It’s stable?”
I checked the monitoring dashboard.
“Yes.”
He exhaled.
“Thank you.”
I looked at him.
“Now we need to talk about my contract.”
He gave a tired laugh.
“Yes.”
He knew exactly what I meant.
The $800 check had never been acceptable.
But I didn’t want revenge.
I wanted the agreement honored.
The original contract required $800,000 upon successful recovery.
The final stability test was now complete.
Martin’s legal team reviewed everything.
There was no loophole.
The payment was owed.
Two weeks later, I received the full $800,000.
The company also paid my legal expenses.
Northbridge Systems was removed from the project.
The CFO resigned before the internal investigation concluded.
The company reported the conflict of interest to its board and insurers.
The suspected sabotage was referred to law enforcement and outside forensic investigators.
I never learned whether every person involved would face criminal charges.
That wasn’t my decision.
My job had been simpler.
Recover the system.
Document what happened.
Protect the evidence.
And leave.
But Martin asked me to stay.
Not as an employee.
As an independent security and recovery consultant.
I declined.
He looked surprised.
“Why?”
“Because I don’t want to spend the rest of my career being called only when everything has already gone wrong.”
He nodded.
“That makes sense.”
I packed my equipment.
Before leaving, I placed the $800 check on his desk.
He looked at it.
“You kept it?”
“I wanted you to see it.”
He smiled sadly.
“Fair enough.”
I left it there.
Not because $800 was meaningful.
Because it represented something.
The company had decided my expertise was worth almost nothing at the exact moment they needed it most.
Then reality had answered for me.
I didn’t shut their network down.
I didn’t sabotage anything.
I didn’t touch the system after I left.
They had built a recovery process dependent on outdated credentials, undocumented procedures, and contractors with conflicting interests.
When the final recovery step failed, their own architecture collapsed.
My only mistake had been assuming they would honor their agreement.
I never made that mistake again.
A year later, I started my own recovery consulting firm.
My first client was a midsize manufacturing company that had lost access to a critical database.
Before I touched anything, I asked one question.
“Who owns the recovery keys?”
They showed me.
“Who can change them?”
They answered.
“Who can authorize emergency access?”
They answered again.
Then I asked the question most companies hate.
“What happens if your only recovery expert quits tomorrow?”
The room went quiet.
I smiled.
“Exactly.”
That became one of the principles of my company.
No critical system should depend on one person.
No recovery process should exist only in someone’s memory.
And no emergency agreement should ever be based on trust alone.
As for the $300 million system, the company eventually rebuilt much of its infrastructure.
The incident cost them far more than the $800,000 they had tried to avoid paying.
Downtime.
Legal fees.
Forensic investigations.
Lost contracts.
Reputation damage.
And months of rebuilding.
But the number I remembered wasn’t $300 million.
It wasn’t $800,000.
It wasn’t even $800.
It was two minutes.
Two minutes between the moment they handed me that insulting check and the moment their network collapsed.
For those two minutes, they thought they had won.
They thought they had saved $799,200.
They thought I was desperate enough to accept whatever they offered.
They were wrong.
I hadn’t been desperate.
I had simply been finished.
And there is a difference.
When they needed me, they treated my expertise like a commodity.
When they thought they had regained control, they tried to reduce my value to $800.
But the moment the system failed, they finally understood what they had actually been paying for.
Not a keyboard.
Not a few hours of troubleshooting.
Not access to some magical secret.
They had been paying for twenty years of experience knowing what to do when everything else stopped working.
And that was something they couldn’t replace with a cheaper check.